Enterprise DNS Security That Protects Every Query
Detect, Block and Control DNS Threats Before They
Reach Your Network
— Why DNS Security Matters
Detect, Block, and Control DNS Threats Before They Reach Your Network
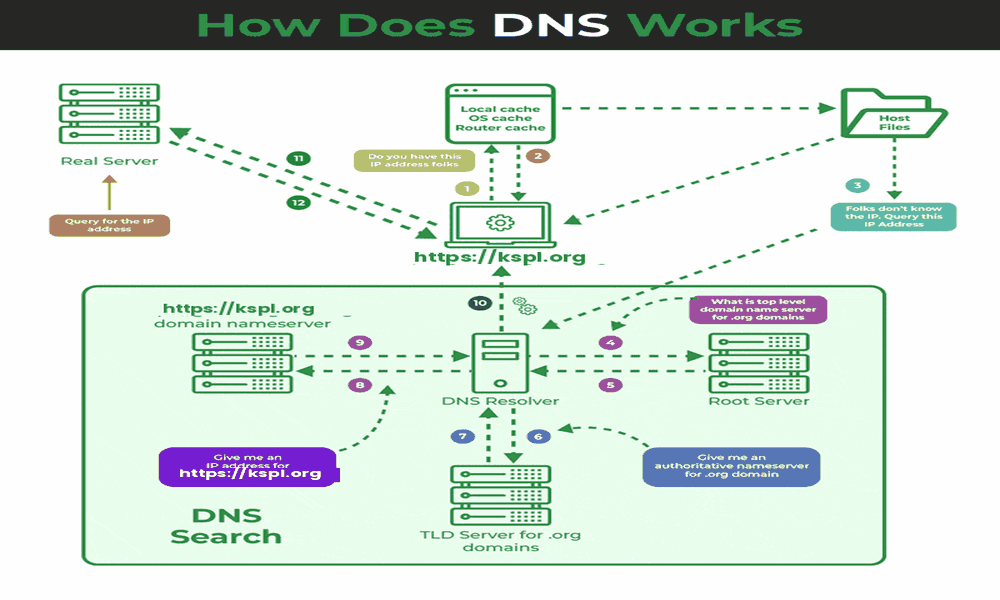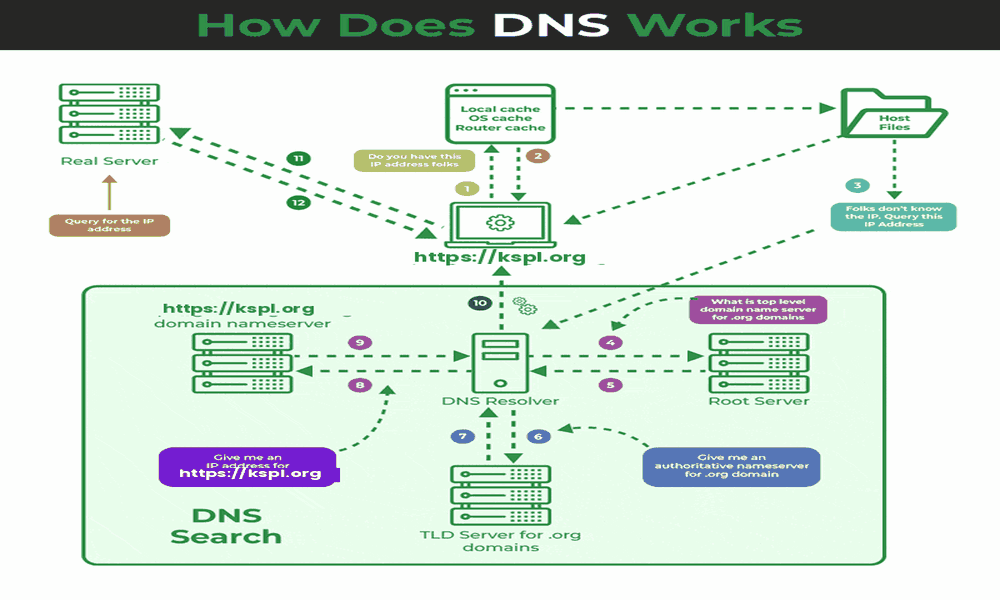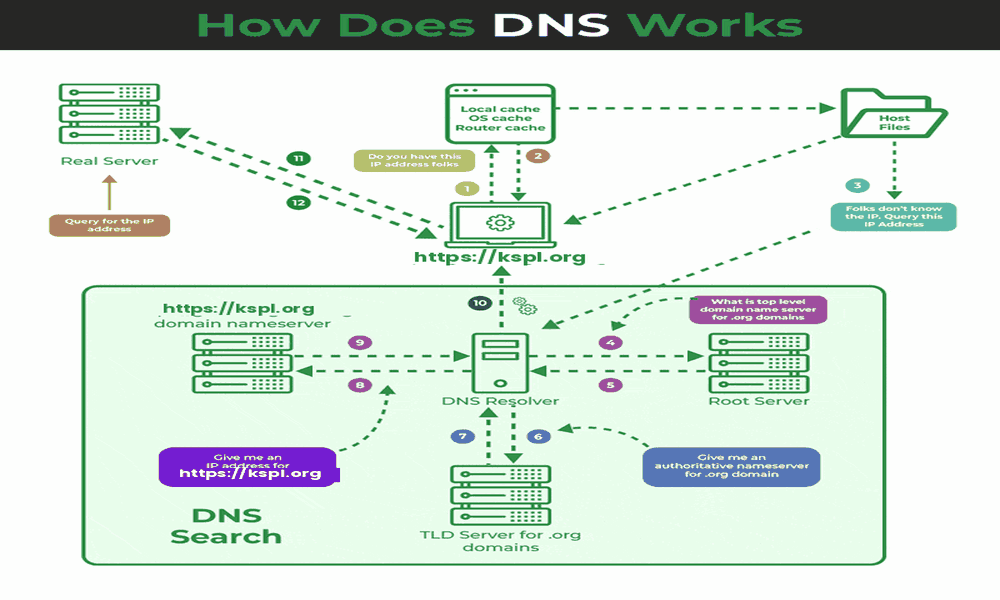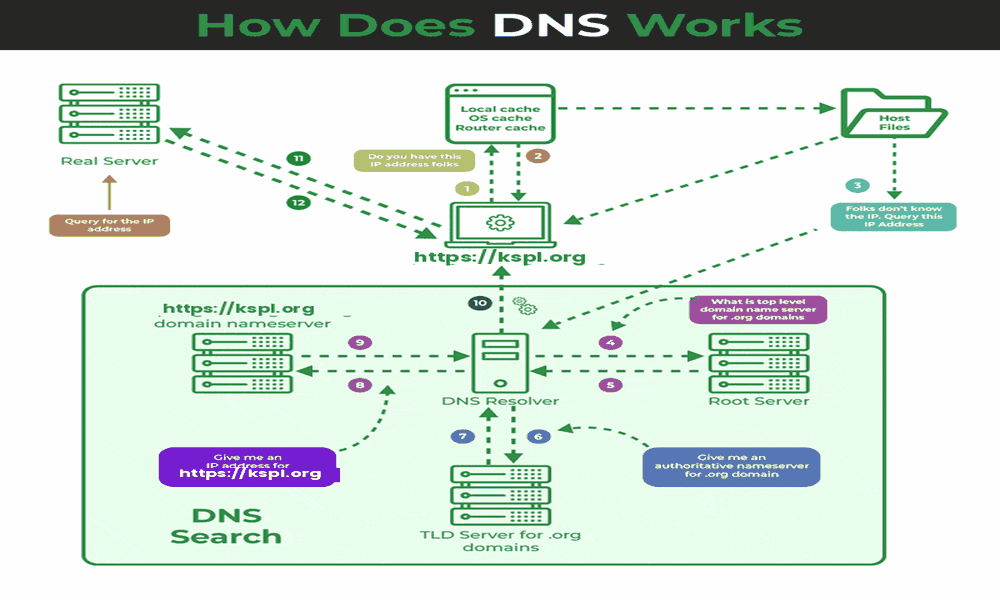
DNS is involved in nearly every connection across an enterprise network — which also makes it one of the most exploited channels for malware communication, phishing, command-and-control (C2) activity, DNS tunneling, and data exfiltration.
KSPL DNS Security embeds enterprise-grade protection directly at the DNS layer. Built on the proven BIND9 architecture and extended with advanced threat detection, policy enforcement, and centralized visibility, the platform helps security teams stop malicious connections before they happen — not after.
DNS Threat Protection Capabilities
Malicious Domain Blocking
Prevents users and systems from resolving domains flagged as malicious, suspicious, or prohibited by policy.
DNS Tunneling Detection
Flags unusual query patterns that may indicate attackers hiding C2 traffic or exfiltrating data inside DNS packets.
DNS Anomaly Detection
Analyzes query frequency, entropy, and lexical structure to surface deviations from normal network behavior.
Phishing & Malicious Domain Protection
Blocks access to known phishing and malware domains at the resolution layer — before a connection is ever established.
Command-and-Control (C2) Detection
Identifies domain communication patterns associated with malware attempting to reach external C2 infrastructure.
Domain Generation Algorithm (DGA) Detection
Uses lexical and behavioral analysis to catch algorithmically generated domains commonly used in malware campaigns.
AI-Assisted DNS Threat Detection
Static blocklists alone can’t keep pace with fast-evolving DNS threats. KSPL strengthens protection with machine learning-based DNS anomaly detection, analyzing each query for suspicious behavioral and domain-level signals, including:
- Domain characteristics and lexical patterns
- Query frequency and temporal bursts
- Entropy and randomness scoring
- Repeated or abnormal DNS requests
- Suspicious client behavior
- Potential command-and-control patterns
- Network-wide DNS anomalies
Complete Visibility Into Enterprise DNS Activity
You can’t secure what you can’t see. KSPL centralized dashboard gives security and operations teams a live view of DNS activity across the network, including:
- DNS query trends — spot shifts in network activity over time
- Top queried domains — identify the most-accessed destinations
- Top DNS clients — trace where queries originate
- Query types — analyze request behavior patterns
- DNS response activity — track resolution trends and failures
- Threat detections — investigate flagged suspicious activity
- Server performance & QPS — monitor DNS infrastructure health
Centralized DNS Management
Manage DNS security policy, logging, and operations from a single unified platform.
Real-Time Threat Detection
Machine learning-based anomaly analysis catches novel DNS threats signature tools miss.
RPZ-Based DNS Firewall
Block or redirect malicious domains directly at the resolver, with no endpoint agents required.
DNSSEC & Encrypted DNS
Validate DNS response authenticity and protect queries in transit with DoT/DoH.
| Industry | Use Case | |
|---|---|---|
| BFSI | Protect DNS supporting banking apps, branch connectivity, and internal services while retaining centralized visibility and control. | |
| Government | Deploy DNS security within controlled infrastructure while keeping full authority over policies, logs, and operations. | |
| Defence | Support private, restricted network environments where infrastructure ownership and operational visibility are non-negotiable. | |
| Telecom | Secure high-volume DNS environments while maintaining visibility into requests and DNS-based threats. | |
| Large Enterprises | Centralize DNS operations and policy across distributed networks, applications, users, and infrastructure. |