DHCP that keeps working when everything else is having a bad day.
DHCP is the first conversation every device has with your network. When it is healthy, nobody notices. When a scope fills up or a server drops, laptops get no address, desk phones can’t register, badge readers go quiet and the helpdesk queue fills up before ten in the morning. Kubernesis DDI runs DHCP as a managed, redundant service across your head office, branches and cloud, with IPAM and DNS updated from the same lease.
— The situation
The scope ran out on a Monday morning.
A branch finished a hiring drive and forty new people joined on the same day. Nobody checked the subnet. The first devices got addresses. Everyone after that got a self-assigned address, no network, and a ticket number.
Two branches away, the DHCP server is a Windows machine under a desk. Failover was set up years ago by someone who has since left. Options are edited by hand on each server, so the desk phones in one office still point to a call server that was retired last year.
— Capabilities
What you get.
Central scope management
Create and change scopes, ranges, exclusions, reservations and options from one console. Changes go to the right servers automatically, so nobody needs to log in to each box.
Failover pairs
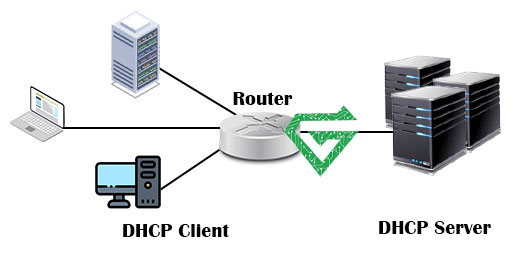
Every critical scope runs on a pair of servers. If one goes down, its partner keeps handing out and renewing leases, and configuration changes are kept in step on both sides.
Branch survivability
Larger branches run DHCP locally, so devices still get addresses when the WAN link drops. Smaller sites are served from the core, with lease times set to ride out routine outages.
Automation and API
Reservations and scopes can be created by your provisioning workflows through a REST API, so a new server or VM gets its address without a ticket.
Lease history with device context
See which device held an address, and when: MAC address, hostname and device type, kept as history. When security asks who had a certain IP at 2:14 a.m. last Tuesday, the answer takes seconds.
Automatic DNS and IPAM updates
A new lease creates the address record and the matching DNS entries. When the lease ends, they are released. No stale records and no second spreadsheet.
— DHCP and security
Every new device introduces itself here first.
Before a device can do anything on your network, it asks DHCP for an address. That makes DHCP one of the earliest and most reliable signals of what has just connected, including devices that no security agent will ever be installed on.
- Unknown devices flagged the moment they request an address
- Lease records forwarded to your SIEM for investigations
- The same device record shared with Kubernesis MDM for enrolment checks
- Combined with Protective DNS, so a suspicious device can be traced to an owner and a location, not just an IP
— Migration
Moving off Windows Server DHCP or ISC DHCP.
Most estates we see run a mix: Windows DHCP at head office, something else at the branches, and a few routers handing out addresses nobody remembers setting up. Moving to one managed service doesn’t need a weekend of risk.
Assess
We import your existing scopes, reservations and options, and hand you a list of overlaps, unused ranges and scopes close to exhaustion.
Design
We decide which sites get local DHCP, which are served centrally, and how failover is paired.
Deploy
Sites are cut over one at a time, with a tested rollback at every step. Lease data comes across, so devices keep their addresses.
Operate
Ongoing support under an agreed SLA, from engineers in Gurugram who already know your topology.
— Deployment
How it lands.
| Site type | DHCP role | If the WAN drops |
|---|---|---|
| Data centre / HQ | HA appliance pair, primary DHCP | Core service stays up on the partner |
| Large branch | Local virtual pair | Leases continue to be issued locally |
| Small branch | Served from the core via relay | Devices keep current leases until renewal |
| Cloud VPC | Addressing tracked in IPAM | Cloud-native services continue |
What is enterprise DHCP management?
It is the practice of running DHCP across all your sites as one centrally managed service, with consistent configuration, redundancy, monitoring and records, rather than as separate servers that each need to be looked after on their own.
What is DHCP failover, and do we need it?
DHCP failover pairs two servers so either one can issue and renew leases for the same scopes. If DHCP stops, new devices can’t join the network and existing ones drop off as leases expire. For any site that matters to the business, failover is worth having.
Can we keep our existing Windows DHCP servers during migration?
Yes. We import their configuration first and cut sites over in stages, so your current servers keep running until each site is ready.
Does it support DHCPv6?
Yes. IPv4 and IPv6 are managed from the same console.
How does DHCP help with security?
Every device asks DHCP for an address before it does anything else. Lease history lets you tie an IP address in an alert back to a specific device, time and location, and unknown devices can be flagged as soon as they connect.
How long does a DHCP migration take?
It depends on the number of sites and how the current setup looks. We always start with an assessment, and you get a site-by-site plan with timings before anything changes.